Policies
Access, data and attacks, approvals, detections, and policy as code.
Configure
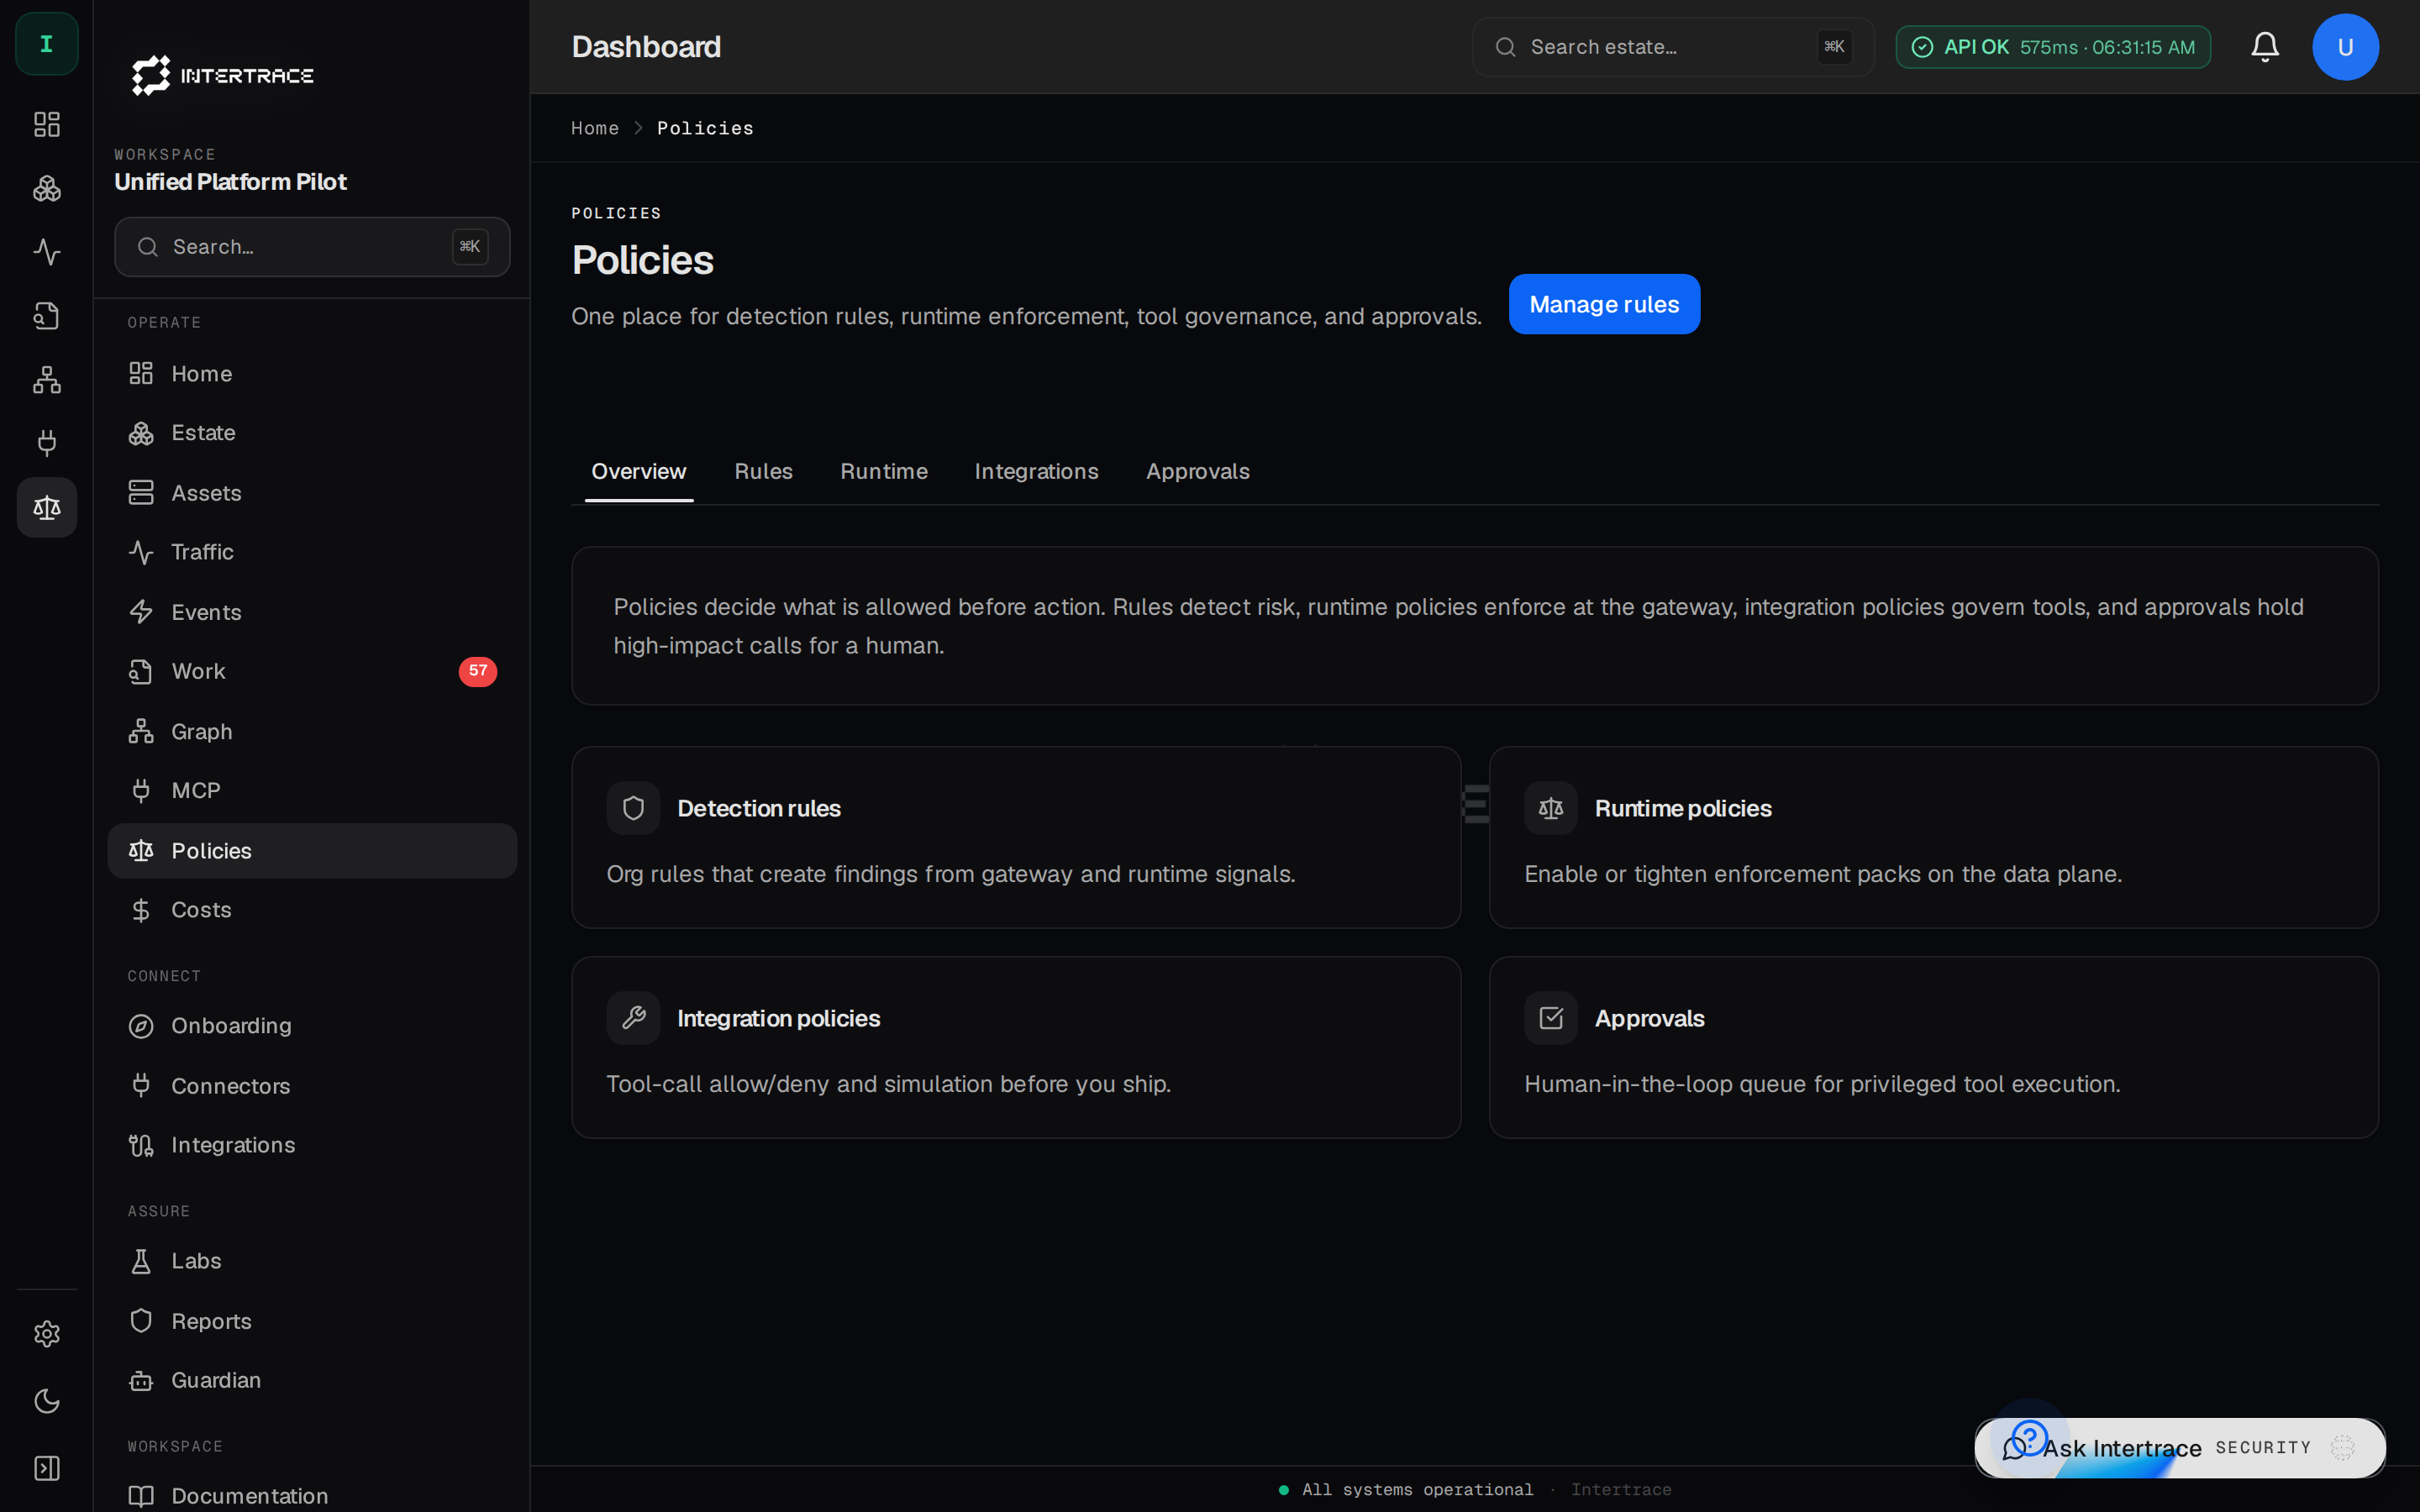
/dashboard/policies has Overview, Access, Data & attacks, Approvals, Detections and Policy as code. Rules layer organization → agent → exception, and an agent can tighten but never loosen what the organization sets. Packs are inputs, not readiness or compliance proof.
The enforcer reads what a call does from its name and arguments (git force pushes, SQL deletes, shell pipes, payments, outbound messages) and gives it a consequence tier. An agent's role sets, per tier, whether calls run, ask in production, always ask, or are blocked. New runtime agents start in a learning period: consequential calls not granted yet ask, and nothing gets looser until a person reviews the proposal and locks it in. Organization guardrails add asks or data rules for every agent, with named exceptions that expire.
Policy as code validates, diffs, and applies YAML: our rules: format or a Preloop v1.0 policy document (imported tighten-only, with a warning for anything it can't map). Credentials in the YAML are a validation error. Applied YAML compiles into the same decisions the gateway already enforces, not a second engine. CLI: itr policy validate|diff|apply, and itr policy agent export|diff|apply for one agent, with an org API key. Control plane.