Introduction
Welcome to the Intertrace docs. Explore quickstarts, client connect guides, dashboard hubs, API reference, and more. Protect AI with AI.
What is Intertrace?
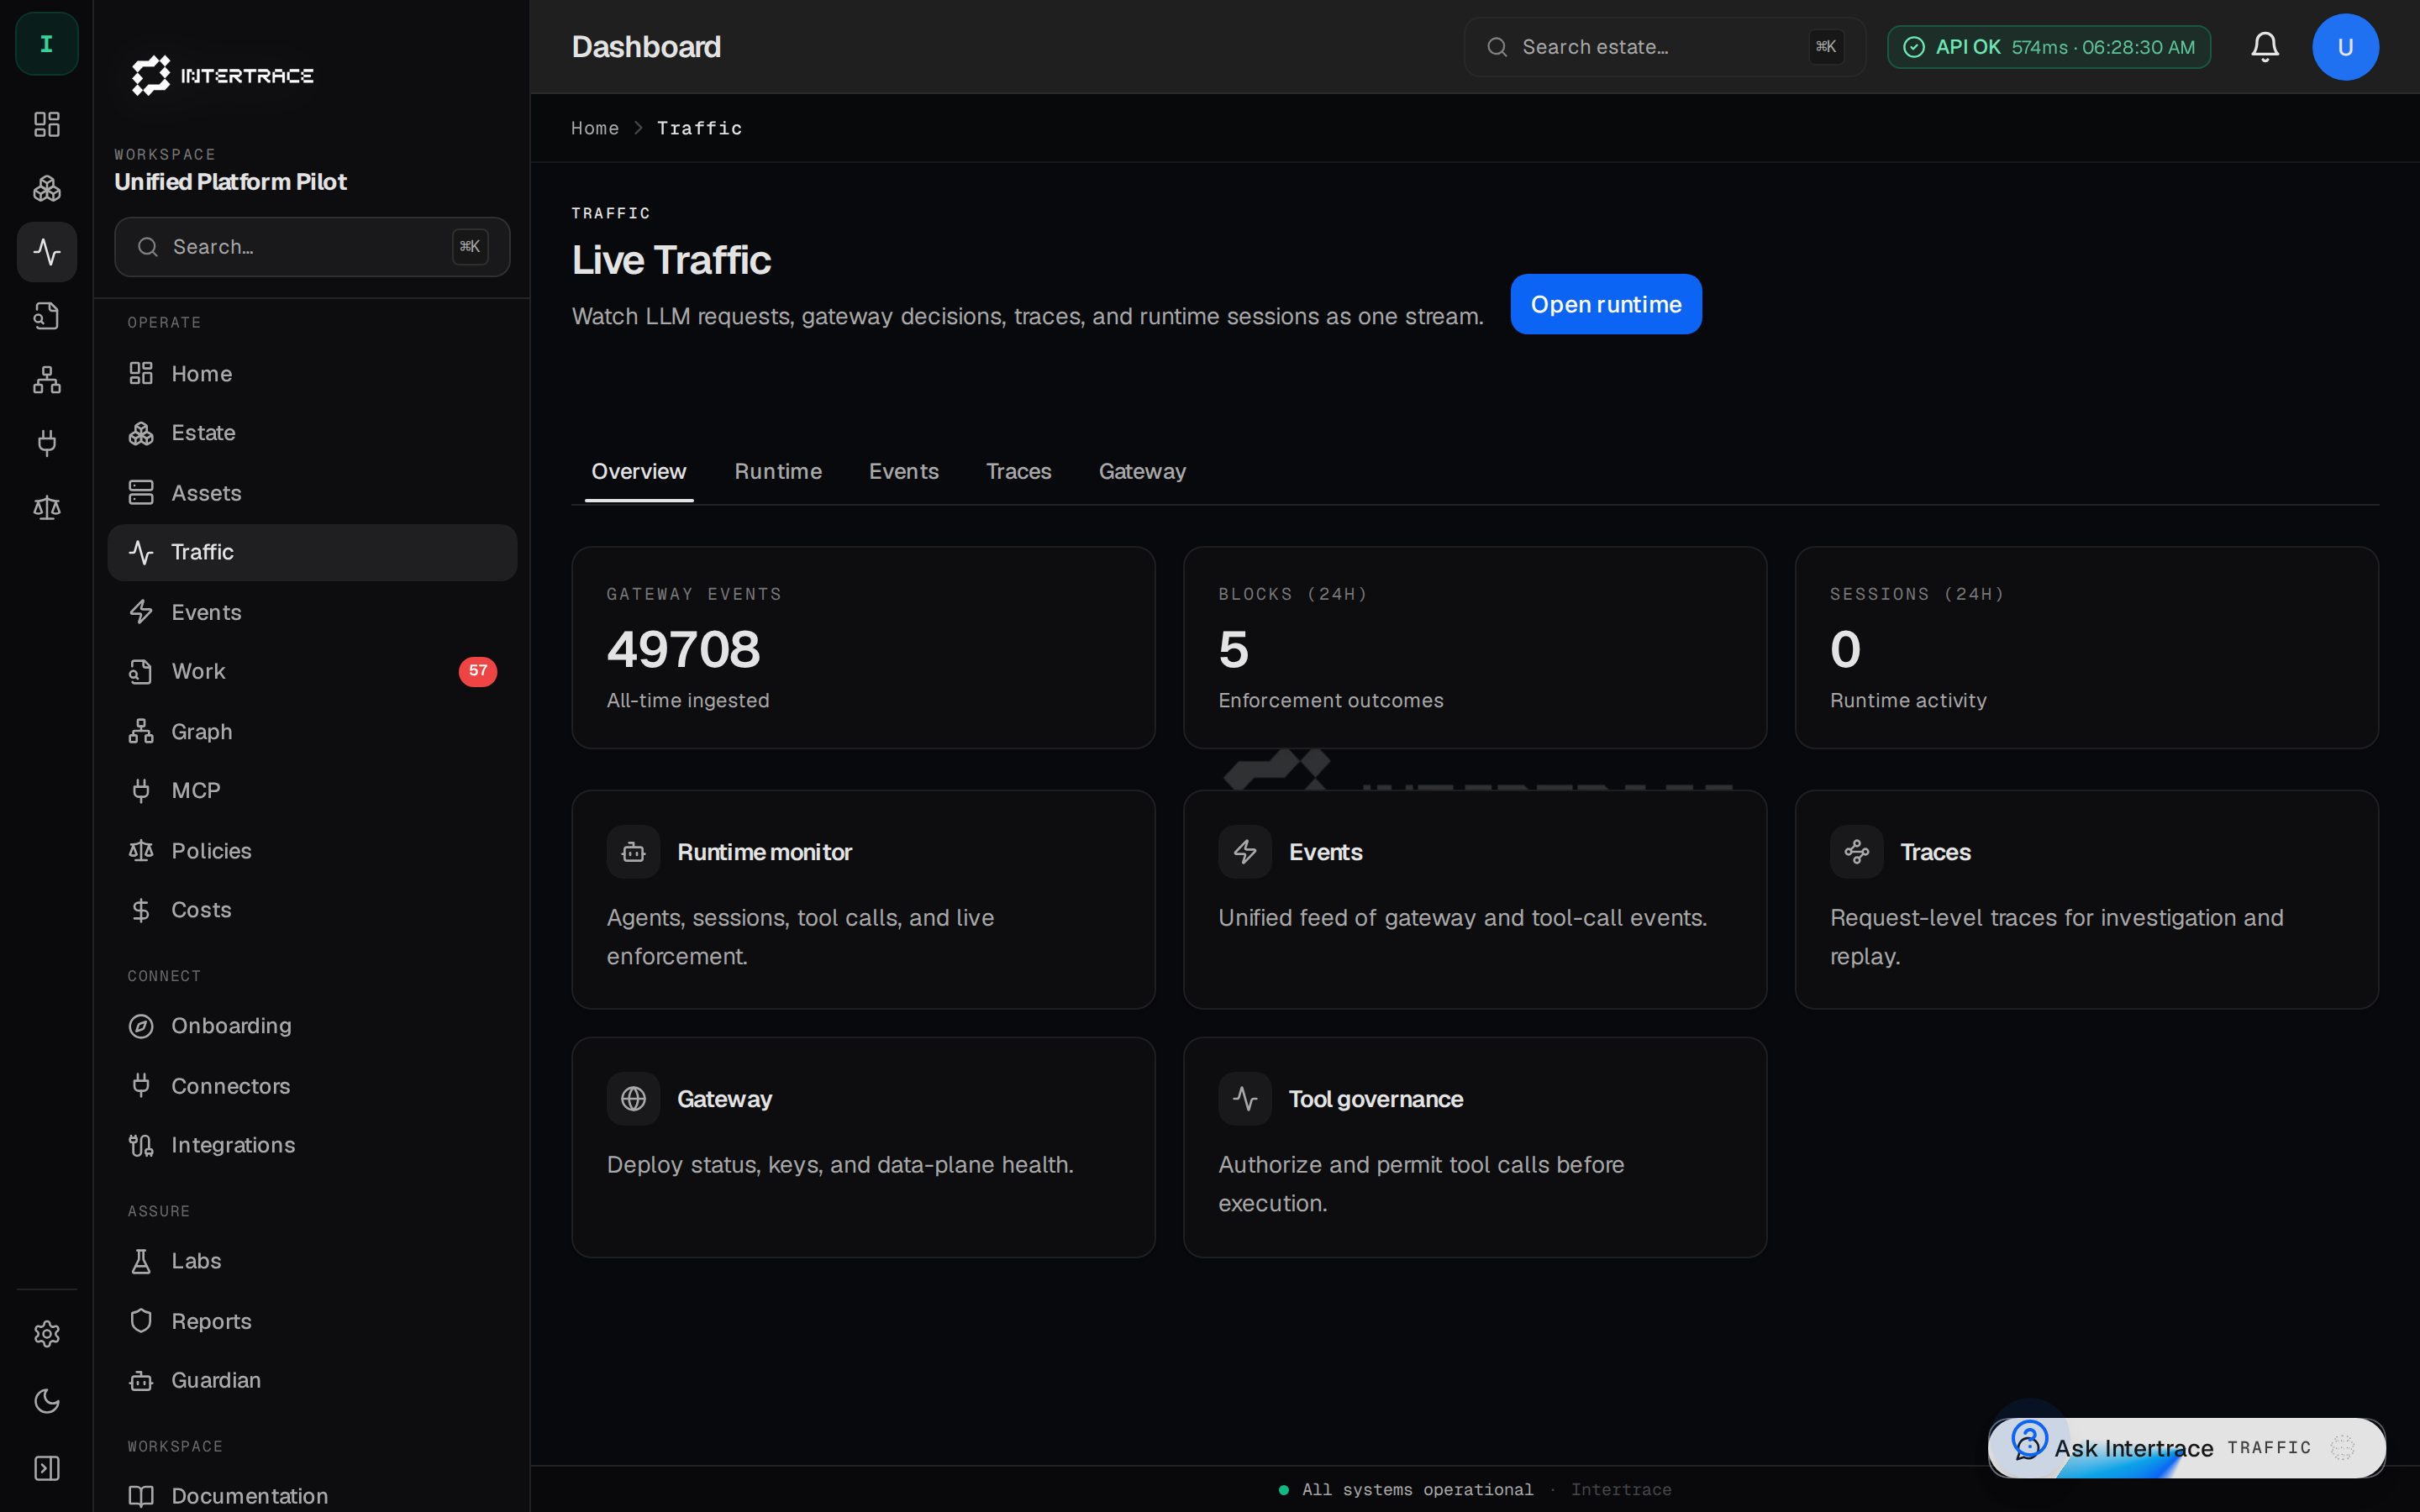
Intertrace is an inline AI security gateway plus a posture management dashboard. Customer apps and agents send model, MCP, and agent-to-agent (A2A) traffic through one hosted gateway that checks prompts, responses, and tool calls; the dashboard stores what happened with org isolation and surfaces findings, assets, gateway events, approvals, and policy controls. Coding agents (Claude Code, Cursor, Codex CLI, GitHub Copilot CLI, OpenCode) are governed through itr connect hooks that ask the same gateway before each tool call.
Start here
Quickstart
Mint a runtime key, point your client at the gateway, send a first request.
Early access & signup
Join the waitlist, get an access code, create your first organization.
Control plane
itr CLI, org API keys, permission hooks, policy gitops, approvals.
Connect clients
Cursor, OpenAI SDK, Claude Desktop, LiteLLM, MCP, and more.
Product spine
Connect → Estate → Traffic → Work → Graph → Policies in the dashboard.
SDKs
npm install @intertrace-runtime/runtime and @intertrace-runtime/tracing.
API reference
OpenAPI, telemetry ingest, and authorize endpoints.
Troubleshooting
Common 401/422/empty-trace issues and how to fix them.
Honest limits
Behavioral baselines need volume and time (typically 7/30/90 day windows) before deviation alerts are trustworthy. Until integration sends traffic, dashboards show empty states with links back to these docs.
Industry solution maturity is computed from evidence. Policy packs and framework mappings are inputs, never compliance proof by themselves.